As Featured in PI Magazine: What the M&A Insider Trading Ring Reveals About Investigating Corporate Information Leaks
We are honored to be featured in PI Magazine where we explain how private investigators can investigate suspected material nonpublic information (MNPI) leaks within corporations, law firms, investment banks, and other organizations.
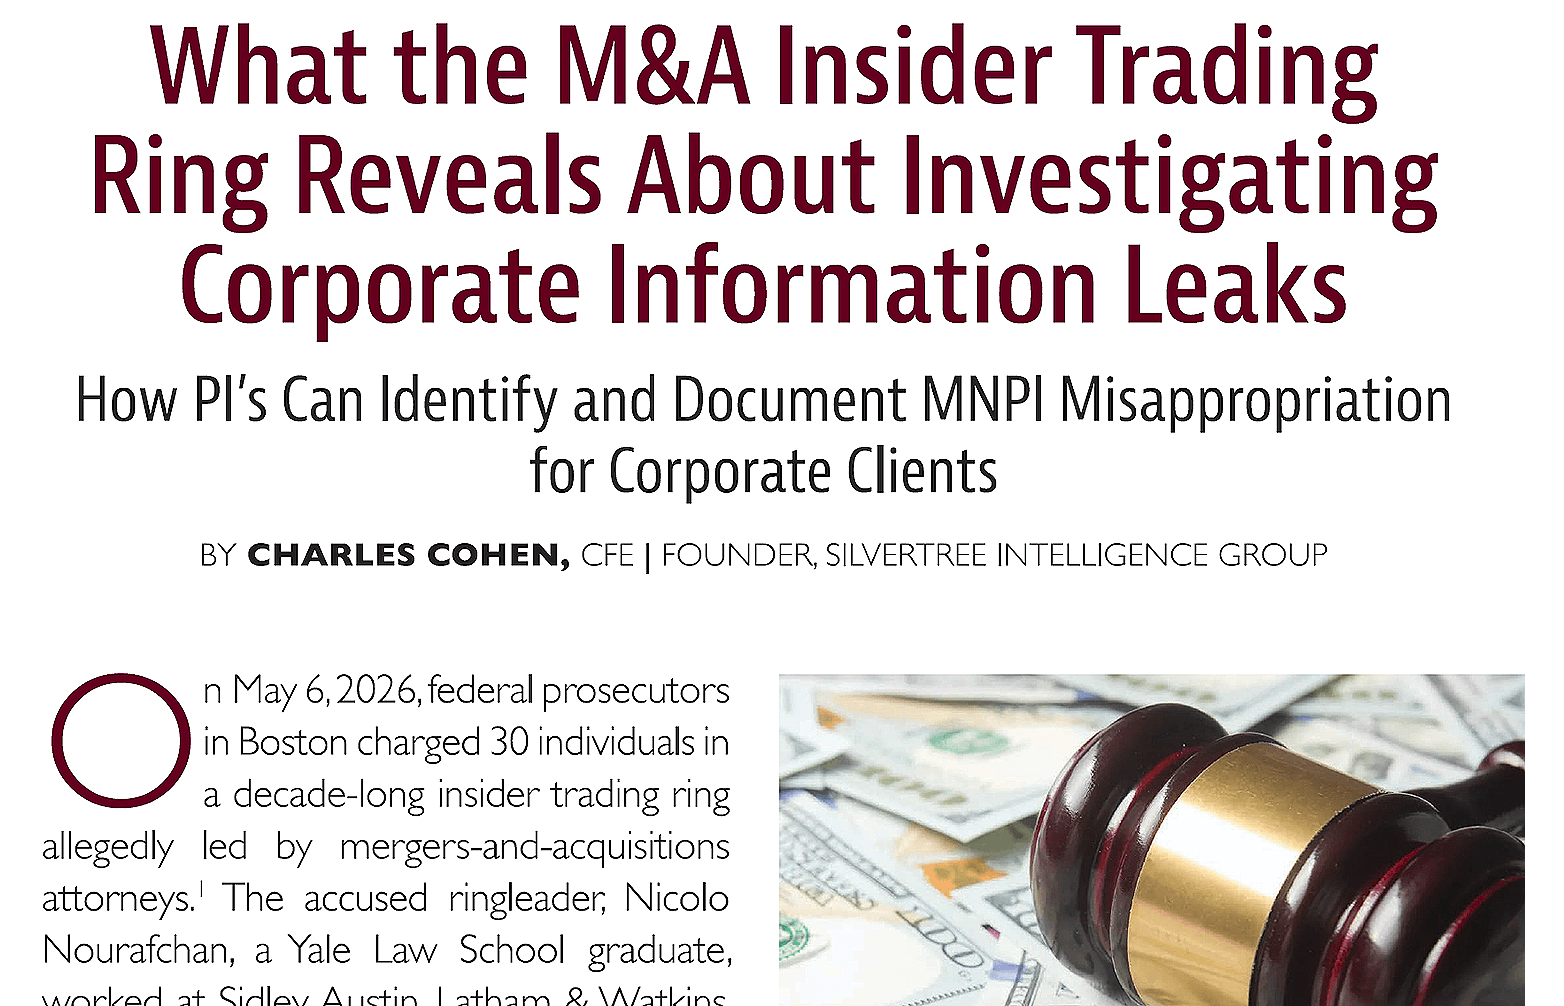
On May 6, 2026, federal prosecutors in Boston charged 30 individuals in a decade-long insider trading ring allegedly led by mergers-and-acquisitions attorneys.¹ The accused ringleader, Nicolo Nourafchan, a Yale Law School graduate, worked at Sidley Austin, Latham & Watkins, Cleary Gottlieb, and Goodwin Procter from 2013 to 2023. Prosecutors allege he accessed confidential deal information from these firms’ internal networks and provided it to relatives, friends, and associates, who traded on it for tens of millions of dollars in illicit profits.²
The defendants used burner phones, encrypted messaging applications, and coded language. They remained undetected for years within institutions known for sophisticated compliance programs. However, the scheme ultimately unraveled because, regardless of the methods used to hide it, data perpetually creates a trail of evidence, even when those involved believe otherwise.
For private investigators working with corporate clients, law firms, or in-house legal teams, this case offers valuable lessons. It demonstrates how material nonpublic information (MNPI) moves within organizations, the methods sophisticated leakers use to conceal their actions, and how investigators can build a documented evidentiary record to support both civil and criminal referrals.
How MNPI Leaks Originate And Travel

Under federal securities law, MNPI is information that has not been publicly disclosed and that a reasonable investor would consider important in making an investment decision.³ In a transactional context — mergers, acquisitions, divestitures, tender offers — this category is expansive: deal terms, target identity, timing, board deliberations, regulatory risk assessments, and financing structures all qualify.⁴
Such leaks rarely originate at the executive level. They more often begin with individuals in privileged but lower-profile roles, such as deal attorneys, paralegals, investment banking analysts, administrative professionals with document management access, and IT staff with backend privileges. The Boston case highlights this: Nourafchan was an associate, not a partner, when the alleged scheme began. His access was routine and transactional, making detection difficult.
Information typically moves in two phases. First, the insider accesses sensitive materials through authorized channels, such as document management systems or deal rooms, and extracts key details. Second, these details are transmitted to external recipients using methods intended to evade monitoring, such as personal devices, encrypted apps, off-site verbal communication, or coded references that bypass keyword-monitoring tools.
The Boston case demonstrates that even highly secure institutions are vulnerable to insiders operating within their authorized access. The primary threat is not external hackers, but trusted individuals who access information legitimately and then misuse it.
Investigative Techniques: Identifying, Documenting, and Attributing the Breach
When a corporate client or law firm retains you to investigate a suspected MNPI leak, your first obligation is to scope the investigation. Before conducting a single interview or reviewing a single log, you need a written engagement letter — ideally structured under attorney-client privilege through retained counsel — defining the universe of potential sources, the time period under review, the systems involved, and the legal standards governing your findings.⁵
The investigative process then divides into three main areas:
Digital Footprint Analysis.
Every document management system, email platform, and file-sharing tool generates metadata. Who opened a file? When? From which device and IP address? Did they print it, forward it, or download it to an external drive? In the Boston case, prosecutors alleged that Nourafchan accessed deal documents while “on leave” from Goodwin Procter — a detail only recoverable through access log review.⁶
At this stage, investigators and digital forensics partners play a critical role. Relevant data often exists but must be preserved through formal requests to prevent overwriting, maintained with chain-of-custody protocols for admissibility, and analyzed with tools that correlate access events across systems. Collaborate with the client’s IT security team or outside forensics counsel to image relevant servers before routine deletion policies remove evidence.⁷
Behavioral and Timeline Correlation.
In MNPI cases, the most compelling evidence is often circumstantial, such as a pattern of access events followed by unusual trading activity in a public company’s securities. Investigators should create detailed timelines that align deal milestones, such as signing NDAs, submitting bids, obtaining board approval, and filing regulatory documents, with access records of potential leakers and trading records of known associates.⁸
Open-source intelligence (OSINT) is essential. Public brokerage disclosures, SEC Form 4 filings, options activity data, and social network analysis can reveal connections between suspected leakers and recipients — connections the leaker may have believed were hidden.
Source Development and Interviews.
Documentary records establish what happened, while sources explain why and how. In law firms or investment banks, potential sources include colleagues who observed unusual behavior, IT staff who noticed anomalous access, and administrative personnel who detected irregular communication patterns.
Conduct interviews under proper legal authority, with counsel present as needed. Document all interactions contemporaneously. In the Boston case, at least nine defendants pleaded guilty before the broader indictment was unsealed, highlighting the value of cooperative witnesses and the fact that immunity negotiations are handled by prosecutors, not investigators.⁹
Structuring Findings for Civil and Criminal Referral
A critical decision in any corporate leak investigation is how to package and deliver findings. Poorly structured reports can compromise SEC referrals, alert subjects prematurely, or create evidentiary issues in litigation. Well-structured reports enable multiple enforcement actions.
Organize your report for three audiences: the client’s internal compliance team, outside counsel preparing a civil claim, and, where appropriate, federal prosecutors or SEC enforcement staff. Each has distinct evidentiary thresholds, discovery exposures, and procedural requirements. Structure findings as a modular document that can be separated as needed.¹⁰
At a minimum, your investigative record should include: a timeline of access events and deal milestones; preserved digital artifacts with documented chain of custody; signed interview memoranda; OSINT documentation of relationships between the suspected leaker and trading counterparties; and a clear summary of remaining evidentiary gaps, specifying what is known, inferred, and what requires further investigation or legal process.
Do not overstate conclusions. The most credible investigative reports clearly acknowledge uncertainty. If evidence shows a specific individual accessed a deal document before an unusual options trade, state that, and specify what remains unproven. Prosecutors and civil litigators can work with a well-documented record that recognizes its limits but cannot rely on reports that overstate findings.
Practitioner Checklist — Corporate MNPI Leak Investigation
Secure written engagement through retained counsel to establish privilege protection.
Issue immediate litigation hold covering document management systems, email, and communication platforms.
Obtain and preserve access logs from all systems containing MNPI (DMS, email, deal rooms, VPN).
Identify all individuals with authorized access to the relevant deal materials during the relevant period.
Correlate access events against deal milestones and publicly available trading activity.
Conduct OSINT on potential leakers: social networks, financial disclosures, and known associates.
Conduct properly predicated and documented interviews of witnesses and potential cooperators.
Maintain strict chain-of-custody protocols for all digital evidence.
Structure findings as a modular report addressable to compliance, civil counsel, and criminal referral separately.
Document evidentiary gaps explicitly — do not overstate conclusions.
The Takeaway for Private Investigators
The Boston case demonstrates that the most damaging corporate information leaks often originate from trusted insiders, not external cyberattacks. These insiders operate within their authorized access and use methods designed to evade monitoring. Law firms, private equity funds, and investment banks are increasingly aware of this risk and are more willing to engage outside investigators when internal compliance teams reach their limits.
Private investigators who understand the MNPI framework can integrate digital forensics, source development, and securities law, and can structure findings for multiple enforcement pathways, providing significant value. The Boston case involved a decade of misconduct, 30 defendants, and leading law firms. If it occurs there, it is likely to happen elsewhere and is currently under investigation.
Resources
U.S. Department of Justice, “Thirty People Charged in Connection with Decade-Long Insider Trading Scheme,” May 6, 2026. https://www.justice.gov/usao-ma
Reuters, “Lawyers, Traders Among 30 Charged in Global Insider Trading Case,” May 6, 2026. https://www.reuters.com
Securities Exchange Act of 1934, Section 10(b); SEC Rule 10b-5, 17 C.F.R. § 240.10b-5. https://www.law.cornell.edu/cfr/text/17/240.10b-5
U.S. Securities and Exchange Commission, “Insider Trading,” Investor.gov.
https://www.investor.govAssociation of Certified Fraud Examiners, Fraud Examiners Manual, 2024 Edition. https://www.acfe.com
Bloomberg Law, “Elite M&A Lawyers Fed Massive Insider-Trading Ring, US Alleges,” May 6, 2026. https://news.bloomberglaw.com
Above the Law, “Former BigLaw Attorney Allegedly ‘Turned His Resumé Into A Decade-Long Insider Trading Operation,’” May 7, 2026. https://abovethelaw.com
National Institute of Standards and Technology, Cybersecurity Framework 2.0, 2024. https://www.nist.gov/cyberframework
U.S. Securities and Exchange Commission, Office of Inspector General, Insider Threat Program Best Practices, 2023. https://www.sec.gov/oig/reports
Federal Bureau of Investigation, “Corporate Insider Threat: A Guide for Private Industry,” 2023. https://www.fbi.gov/file-repository/insider-threat-brochure.pdf
